Usable hosts
Subnet calculator for IPv4 and IPv6
Type a CIDR, a subnet mask, a wildcard or an address range. Results appear as you type, with every value one click from your clipboard.
- Runs entirely in your browser
- No ads, no cookies, no sign-up
- Special-purpose ranges from the IANA registries
- IPv4 · IPv6
Try 192.168.1.10 255.255.255.0 or 10.0.0.5 - 10.0.0.90
Examples
Total addresses
Usable range
Network bitsHost bitsBoundaryClick any bit to move the boundary there.
Addresses
Type
Notation
Name resolution
Split
Split a block and see it.
Start from the result above. Split any block in half, join halves back, and see how the space is shared. Up to 64 blocks on the web.
Enter a CIDR above to split it.
Base block
| # | Block | Usable range | Hosts | Name | Actions |
|---|
Names here disappear when you close the tab. In SubnetDeck, each site keeps its plan — segment names, sizes and VLSM allocation — in folders by customer or project.
See SubnetDeckCheat sheet
Subnet mask cheat sheet.
Every IPv4 prefix with its mask, wildcard and host count, plus the IPv6 sizes you meet in practice. Click a row to calculate it.
| Prefix | Subnet mask | Wildcard | Addresses | Usable hosts | Fits | Typical use |
|---|---|---|---|---|---|---|
| /0 | 0.0.0.0 | 255.255.255.255 | 4,294,967,296 | 4,294,967,294 | 16,777,216 × /24 | |
| /1 | 128.0.0.0 | 127.255.255.255 | 2,147,483,648 | 2,147,483,646 | 8,388,608 × /24 | |
| /2 | 192.0.0.0 | 63.255.255.255 | 1,073,741,824 | 1,073,741,822 | 4,194,304 × /24 | |
| /3 | 224.0.0.0 | 31.255.255.255 | 536,870,912 | 536,870,910 | 2,097,152 × /24 | |
| /4 | 240.0.0.0 | 15.255.255.255 | 268,435,456 | 268,435,454 | 1,048,576 × /24 | |
| /5 | 248.0.0.0 | 7.255.255.255 | 134,217,728 | 134,217,726 | 524,288 × /24 | |
| /6 | 252.0.0.0 | 3.255.255.255 | 67,108,864 | 67,108,862 | 262,144 × /24 | |
| /7 | 254.0.0.0 | 1.255.255.255 | 33,554,432 | 33,554,430 | 131,072 × /24 | |
| /8 | 255.0.0.0 | 0.255.255.255 | 16,777,216 | 16,777,214 | 65,536 × /24 | 10.0.0.0/8 private block |
| /9 | 255.128.0.0 | 0.127.255.255 | 8,388,608 | 8,388,606 | 32,768 × /24 | |
| /10 | 255.192.0.0 | 0.63.255.255 | 4,194,304 | 4,194,302 | 16,384 × /24 | |
| /11 | 255.224.0.0 | 0.31.255.255 | 2,097,152 | 2,097,150 | 8,192 × /24 | |
| /12 | 255.240.0.0 | 0.15.255.255 | 1,048,576 | 1,048,574 | 4,096 × /24 | 172.16.0.0/12 private block |
| /13 | 255.248.0.0 | 0.7.255.255 | 524,288 | 524,286 | 2,048 × /24 | |
| /14 | 255.252.0.0 | 0.3.255.255 | 262,144 | 262,142 | 1,024 × /24 | |
| /15 | 255.254.0.0 | 0.1.255.255 | 131,072 | 131,070 | 512 × /24 | |
| /16 | 255.255.0.0 | 0.0.255.255 | 65,536 | 65,534 | 256 × /24 | Campus or a large site; 192.168.0.0/16 |
| /17 | 255.255.128.0 | 0.0.127.255 | 32,768 | 32,766 | 128 × /24 | |
| /18 | 255.255.192.0 | 0.0.63.255 | 16,384 | 16,382 | 64 × /24 | |
| /19 | 255.255.224.0 | 0.0.31.255 | 8,192 | 8,190 | 32 × /24 | Large site or cloud network |
| /20 | 255.255.240.0 | 0.0.15.255 | 4,096 | 4,094 | 16 × /24 | Large site or cloud network |
| /21 | 255.255.248.0 | 0.0.7.255 | 2,048 | 2,046 | 8 × /24 | |
| /22 | 255.255.252.0 | 0.0.3.255 | 1,024 | 1,022 | 4 × /24 | Mid-size office, wired plus Wi-Fi |
| /23 | 255.255.254.0 | 0.0.1.255 | 512 | 510 | 2 × /24 | Wi-Fi with many devices |
| /24 | 255.255.255.0 | 0.0.0.255 | 256 | 254 | 1 in a /24 | Standard LAN segment |
| /25 | 255.255.255.128 | 0.0.0.127 | 128 | 126 | 2 in a /24 | Half a /24 |
| /26 | 255.255.255.192 | 0.0.0.63 | 64 | 62 | 4 in a /24 | Servers or management (up to 62) |
| /27 | 255.255.255.224 | 0.0.0.31 | 32 | 30 | 8 in a /24 | Small segment such as printers |
| /28 | 255.255.255.240 | 0.0.0.15 | 16 | 14 | 16 in a /24 | Small DMZ |
| /29 | 255.255.255.248 | 0.0.0.7 | 8 | 6 | 32 in a /24 | Router or firewall segment |
| /30 | 255.255.255.252 | 0.0.0.3 | 4 | 2 | 64 in a /24 | Point-to-point link (traditional) |
| /31 | 255.255.255.254 | 0.0.0.1 | 2 | 2 | 128 in a /24 | Point-to-point link (RFC 3021) |
| /32 | 255.255.255.255 | 0.0.0.0 | 1 | 1 | 256 in a /24 | Single host, loopback |
IPv4 prefixes /8 to /32. Usable hosts subtract the network and broadcast addresses, except /31 and /32.
| Prefix | /64 subnets | Addresses | Typical use |
|---|---|---|---|
| /32 | 4,294,967,296 | 296 | Typical allocation to a provider |
| /40 | 16,777,216 | 288 | Large organization |
| /48 | 65,536 | 280 | One site or organization |
| /52 | 4,096 | 276 | Medium site |
| /56 | 256 | 272 | Small site |
| /60 | 16 | 268 | Small home network |
| /64 | 1 | 264 | One LAN segment (needed for SLAAC) |
| /112 | — | 65,536 | Some point-to-point and service networks |
| /126 | — | 4 | Point-to-point link (older practice) |
| /127 | — | 2 | Point-to-point link (RFC 6164) |
| /128 | — | 1 | Single host, loopback |
Common IPv6 prefix sizes. IPv6 has no broadcast, so every address in a block is usable.
Learn
Why the numbers work out.
Ten of the 11 topics from SubnetDeck's Learn tab, in full. Each explains a mechanism rather than a rule to memorize.
01Masks and Prefix LengthsTwo Ways to Write the Same Boundary
A subnet mask and a prefix length are two ways of writing the same boundary. 255.255.255.0 and /24 mean the same thing. What this boundary divides, and why it can only be written as an integer, becomes clear when you go back to the underlying 32 bits.
A subnet mask and a prefix length are two ways of writing the same boundary. 255.255.255.0 and /24 mean the same thing. What this boundary divides, and why it can only be written as an integer, becomes clear when you go back to the underlying 32 bits.
An IPv4 address is a 32-bit number. Which of those 32 bits identify the network and which identify a device within it is not recorded in the address itself. The position of the boundary is given separately, by the subnet mask.
A subnet mask is a sequence of 32 bits, like the address, with the network bits set to 1 and the host bits set to 0. Written in binary, 255.255.255.0 is 24 ones followed by 8 zeros. The prefix length expresses those 24 ones as a single number, written as /24 here. The two are different notations for the same boundary and point to the same position.
The ones in a mask must be contiguous from the left. RFC 1812 (June 1995) makes this a requirement, and a pattern with zeros between the ones cannot be handled by routing today. The reason lies in how matching works. Deciding whether a destination belongs to a network takes a single comparison: do the n high-order bits match? If the ones are contiguous, the boundary can be expressed as the single number n, and the comparison is a prefix match. With a scattered pattern, the set of bits to compare has to be carried separately; when several routes match, there is no way to decide which one to use, and multiple ranges cannot be combined into one either.
A prefix length is therefore an integer from 0 to 32, and a boundary cannot fall partway through a bit. The number of bits left for hosts is 32 minus the prefix length.
Key points
- 255.255.255.0 and /24 are two notations for the same boundary. Whichever form is entered, the resulting network is the same.
- A wildcard mask is a pattern in which 0 and 1 play the opposite roles to those in a subnet mask. A 0 bit marks a position that must match; a 1 bit marks a position whose value does not matter. It is not the same thing as a subnet mask.
- IPv6 has no dotted mask notation; the boundary is expressed by the prefix length alone.
- A prefix length alone does not identify a network. /24 indicates only where the boundary lies; the actual network is determined together with the address.
02Network and Broadcast AddressesWhy Two Are Subtracted
Every subnet has two addresses that cannot be assigned to devices: the network address and the broadcast address. Because these two are excluded, the number of usable hosts is two less than the total. Why it is these two becomes clear from the pattern of bits in the host portion.
Every subnet has two addresses that cannot be assigned to devices: the network address and the broadcast address. Because these two are excluded, the number of usable hosts is two less than the total. Why it is these two becomes clear from the pattern of bits in the host portion.
Two addresses in a subnet cannot be assigned to devices: the one whose host bits are all 0 and the one whose host bits are all 1.
The address with all host bits set to 0 is called the network address and serves as an identifier for the subnet itself. Notations written in a routing table, such as 192.168.10.0/24, take this form. If this address were assigned to a single device, the pattern that refers to the whole network and the pattern that refers to one device in it would be identical. With no way to tell the two apart, the address is excluded from allocation.
The address with all host bits set to 1 is called the broadcast address and is used to address every device on that subnet at once. RFC 919 and RFC 922 (both October 1984) define this format. Because the pattern exists to reach several recipients at the same time, it cannot be assigned to one particular device.
With these two excluded, the number of usable hosts is the total number of addresses minus 2. A /24 gives 256 − 2, or 254, and a /26 gives 64 − 2, or 62.
The rule of thumb “the lowest and the highest address” merely restates the result. The definition lies in the pattern of the host bits, and the numeric order follows from it.
Key points
- The network address and the broadcast address are determined by whether the host bits are all 0 or all 1. Being the numerically lowest and highest is a consequence of that.
- The same address plays a different role when the prefix length changes. 192.168.10.64 is the network address in a /26, but in a /24 it is an address that can be assigned to a device.
- IPv6 has no broadcast. Sending to all nodes is done by multicast, so there is no need to subtract the last address.
- For /31 and /32, this subtraction does not hold as is. Applied literally, it gives 0 for a /31 and a negative number for a /32, which does not match how they are actually handled.
03/31 and /32Why the Subtraction Breaks Down
The number of usable hosts in a subnet is found by subtracting two addresses, the network address and the broadcast address, from the total. Applied as is to a /31, this calculation gives 0, and for a /32 it gives a negative number. In practice, however, a /31 is treated as 2 and a /32 as 1. This is because, for /31 and /32, the premise of the subtraction does not hold.
The number of usable hosts in a subnet is found by subtracting two addresses, the network address and the broadcast address, from the total. Applied as is to a /31, this calculation gives 0, and for a /32 it gives a negative number. In practice, however, a /31 is treated as 2 and a /32 as 1. This is because, for /31 and /32, the premise of the subtraction does not hold.
The host count can be found as “total addresses − 2” because the address with all host bits 0 refers to the network address and the address with all host bits 1 is reserved as the broadcast address. These two are not assigned to any particular device.
In a /30, two of the four addresses go to these roles and the remaining two are assigned to hosts. When a point-to-point link (a link with only two devices, one facing the other) is expressed as a /30, the link occupies four addresses, of which two are assigned to devices.
RFC 3021 (December 2000) specified that, only when such a link is expressed as a /31, the subtraction does not apply. On a point-to-point link, a packet sent by one end is always received by the other. Since there is no need to address “everyone on this subnet”, there is no reason to have a broadcast address. The address with all host bits 0 was also used as a broadcast destination in an older form, and it no longer has that role. RFC 3021 specifies that both of these addresses are interpreted as host addresses. As a result, both addresses of a /31 are assigned to hosts, and the number of usable hosts is 2. The stated purpose is to reduce consumption of address space.
Note that whether a /31 can be interpreted depends on the implementation. Being specified in an RFC is not the same as being supported by every device.
For a /32, the reason is different. It is only one address wide, so there is nothing to divide into a network address and a broadcast address. That single address is used to represent a route to exactly one address (a host route) or a loopback interface, which has no physical port. The number of usable hosts is 1.
Key points
- A /31 has 2 usable hosts because a point-to-point link never needs a broadcast address. It is not counted as 2 simply because there are two addresses.
- The 1 for a /32 is not the result of a subtraction. With nothing to divide, the rule never applies, and one address remains.
- Some subnet calculators show both a /31 and a /32 as 0. They apply the rule of subtracting 2 from the total uniformly to every length.
- RFC 3021 covers point-to-point links. Links with three or more devices attached are not within its scope.
04Private Addresses and Reserved RangesRanges Set Aside for Specific Uses
Within the 32-bit address space, several ranges have predetermined uses. Private addresses, which can be used freely inside an organization, are one of them; routes to them are not advertised on the internet. The ranges are defined in more than one document, and ranges can be nested inside one another.
Within the 32-bit address space, several ranges have predetermined uses. Private addresses, which can be used freely inside an organization, are one of them; routes to them are not advertised on the internet. The ranges are defined in more than one document, and ranges can be nested inside one another.
Some ranges of the IPv4 address space are excluded from normal allocation because their uses have been decided in advance. The best-known example is private addresses.
RFC 1918 (February 1996) set aside three ranges for use inside organizations: 10.0.0.0/8, 172.16.0.0/12 and 192.168.0.0/16. Routes to these ranges are not advertised on the internet. Separate organizations can therefore use the same addresses at the same time without affecting each other. Conversely, when networks of different organizations are connected directly, the same addresses can appear on both sides.
Other ranges also have defined uses. 127.0.0.0/8 is loopback, referring to the device itself; 169.254.0.0/16 is link-local, used for automatic address configuration; 192.0.2.0/24, 198.51.100.0/24 and 203.0.113.0/24 are reserved for examples in documentation; and 100.64.0.0/10 is set aside for address sharing within service provider networks. The framework that organizes these ranges is defined by RFC 6890 (April 2013).
Ranges can be nested. 240.0.0.0/4 is a large range reserved for future use, but 255.255.255.255/32, which lies inside it, is defined separately as the limited broadcast address. To determine which range an address belongs to, take the matching range with the longest prefix length. Settling on a shorter match as soon as it is found gives a different result.
Key points
- The three RFC 1918 ranges differ in size. 10.0.0.0/8 contains 16,777,216 addresses, 172.16.0.0/12 contains 1,048,576 and 192.168.0.0/16 contains 65,536.
- 172.16.0.0/12 covers 172.16.0.0 through 172.31.255.255. 172.32.0.0 is not in this range.
- An address in 169.254.0.0/16 may have been self-assigned by a device that failed to obtain one automatically. It is not necessarily one that was configured.
- Ranges with defined uses can be added. 100.64.0.0/10 was added in 2012 by RFC 6598.
05Reachability Beyond the Domain and Router ForwardingTwo Attributes of Special-Purpose Addresses
Address ranges with defined uses are registered not only with a name and a reference document but also with attributes that say how they are to be handled. May packets reach the internet? May routers forward them? These two attributes combine differently from range to range and cannot be inferred from the name.
Address ranges with defined uses are registered not only with a name and a reference document but also with attributes that say how they are to be handled. May packets reach the internet? May routers forward them? These two attributes combine differently from range to range and cannot be inferred from the name.
IANA collects address ranges with defined uses in its special-purpose address registry. Besides a name and the RFC it is based on, each range carries five attributes, such as whether it may be used as a source or as a destination. The framework for these attributes was set out by RFC 6890 and revised by RFC 8190 (June 2017). Of the five, the two used directly in design and operational decisions are router forwarding and reachability beyond the domain.
Router forwarding indicates whether a router may pass a packet destined for the range from one interface to another. The link-local range 169.254.0.0/16 is “not forwarded”, so it never leaves its segment. Using an address in this range, a device can communicate only with peers on the same segment.
Reachability beyond the domain indicates whether a packet may cross the boundary of the area an organization manages (its administrative domain). The three RFC 1918 ranges may be forwarded, but they do not reach beyond the domain. They may be carried in routing inside an organization, but address translation is needed to send them outside. 100.64.0.0/10 has the same combination, and is handled the same way even though it is not part of RFC 1918.
The combination is not determined by the name. Some special-purpose ranges do reach beyond the domain. 192.31.196.0/24 (AS112) is used on the internet to absorb reverse lookup queries for private addresses and similar ranges. Dropping every special-purpose range at the boundary would stop ranges like this one too. For some ranges, such as 2002::/16 (6to4), reachability is not specified by the registry.
Key points
- The two attributes describe how a range is treated when it is used as a destination. Whether it may be used as a source is registered as a separate attribute.
- “Not reachable” does not mean a range cannot be used inside an organization. The RFC 1918 ranges may be forwarded within an organization.
- When deciding which ranges to drop at the boundary, look at the reachability value, not the range's name. Ranges that do reach outside are then not stopped by mistake.
- Attributes can be updated as ranges are added or reviewed. When relying on them for a decision, check the date the registry was last updated.
06CIDR and AggregationWhat Follows from Placing the Boundary Freely
IPv4 addresses once had their boundary fixed by their leading bits, and only three kinds of division were available. CIDR dropped this fixed scheme and changed to stating the boundary explicitly with a prefix length. As a result, aggregation, which combines several ranges into one, became possible.
IPv4 addresses once had their boundary fixed by their leading bits, and only three kinds of division were available. CIDR dropped this fixed scheme and changed to stating the boundary explicitly with a prefix length. As a result, aggregation, which combines several ranges into one, became possible.
Before 1993, IPv4 addresses were handled within a framework of classes. The leading bits of an address showed which class it belonged to, and the class in turn fixed the position of the boundary. The units allocated for use on the internet were limited to network portions of 8, 16 or 24 bits.
Under this scheme, allocation is coarse-grained. For an organization that needs to accommodate 500 devices, a range of 256 addresses is not enough, and the next option is a range of 65,536. In addition, because each organization receives a range of its own, the number of entries in routing tables grows in proportion to the number of allocations.
CIDR, defined in RFC 1518 and RFC 1519 (both September 1993), dropped the fixed class boundaries and switched to a scheme that states the prefix length explicitly. The boundary can be placed anywhere from 0 to 32.
Once the boundary was free, several ranges could be written as a single notation. This is aggregation. 192.168.0.0/24 and 192.168.1.0/24 together can be written as 192.168.0.0/23. There are conditions, however: the ranges must be contiguous, their combined size must be a power of 2, and the first address must be a multiple of the combined size. 192.168.1.0/24 and 192.168.2.0/24 are next to each other, but because 192.168.1.0 does not sit on a /23 boundary, they cannot be combined into one.
Key points
- Whether ranges can be aggregated is not decided only by whether they are next to each other. The first address must sit on a boundary of the combined size.
- When several routing table entries match the same destination, the one with the longest prefix length is chosen. An aggregated range and an entry for part of it can therefore coexist.
- The term class survives in documents, but it plays no part in deciding boundaries. Calling a /24 a Class C reflects nothing more than a match in size.
- Aggregation combines notation; the number of addresses does not change. Two /24 blocks hold 512 addresses, and a /23 also holds 512.
07Five Kinds of OverlapWhy Blocks Never Overlap Halfway
The relation between two CIDR blocks always falls into one of five kinds: identical, contains, contained, adjacent or disjoint. A state in which blocks overlap only partly never occurs. This follows from the way blocks are formed; it is not something omitted for the convenience of classification.
The relation between two CIDR blocks always falls into one of five kinds: identical, contains, contained, adjacent or disjoint. A state in which blocks overlap only partly never occurs. This follows from the way blocks are formed; it is not something omitted for the convenience of classification.
A CIDR block has two constraints: its size is a power of 2, and its first address is a multiple of its own size. A range that does not sit on such a boundary cannot be written in prefix notation at all.
These constraints limit how two blocks can relate. If they are the same size, the ranges either match exactly or do not intersect at all. Now take blocks of different sizes, and call the larger one A and the smaller one B. A starts at a multiple of its own size, and that size is divisible by B's size, because both are powers of 2 and B is smaller than A. A therefore divides cleanly into parts the same size as B. Since B also sits on a boundary, it either matches one of those parts of A exactly or lies outside A. It cannot be placed so that it sticks out.
As a result, the possible relations are the following five. If the ranges are exactly the same, the blocks are identical. If one completely contains the other, the relation is contains or contained. If they do not intersect and the end of one touches the start of the other, they are adjacent. If they do not even touch, they are disjoint.
Creating a half overlap would require shifting the start of one block off its boundary. A shifted range cannot be expressed in prefix notation, so it does not exist as a CIDR block.
Key points
- Adjacent is one of the relations in which the blocks do not intersect. The only difference from disjoint is whether the address after the last address of one block is the first address of the other.
- Adjacent blocks cannot always be combined into one. That works only when their combined size is a power of 2 and the start lies on the new boundary.
- Two blocks with the same prefix length either match or do not intersect. A containment relation never arises between them.
- These five kinds are the same in IPv6. The constraints come from the properties of size and boundaries and do not depend on the length of the address.
08VLSM and FLSMDividing into Equal Lengths or by What Is Needed
When one range is divided into several, it can be cut into pieces of the same size, or the size can vary with what each piece needs. The former is called FLSM and the latter VLSM. The difference between them is not the effort involved but what is left over once the range has been divided.
When one range is divided into several, it can be cut into pieces of the same size, or the size can vary with what each piece needs. The former is called FLSM and the latter VLSM. The difference between them is not the effort involved but what is left over once the range has been divided.
FLSM is a method that divides the original range into pieces of equal size. Each additional bit of prefix length doubles the number of pieces, so the number of pieces is limited to a power of 2, such as 2, 4 or 8. Because every piece is the same size, the size is set by the piece that needs the most addresses. The other pieces are given that same size.
VLSM is a method that uses a different prefix length for each piece. For each piece, the number of devices it needs plus two, for the network address and the broadcast address, is rounded up to a power of 2. When pieces are laid out along the boundaries from largest to smallest, the start of each piece always lands on a multiple of its own size, so no unusable gaps appear between them. When smaller pieces are placed first, space before a larger piece that comes later may be left empty so that the larger piece can sit on its boundary.
For VLSM to work, routing information must include the prefix length. Because the length differs from piece to piece, the boundary cannot be recovered from the address alone. Routing schemes that did not carry the length could not mix lengths within a single range.
What is left over after dividing differs. With FLSM, pieces with smaller requirements end up with spare addresses. With VLSM, spare addresses are less likely, but the position of the boundary varies from piece to piece.
Key points
- The number of FLSM pieces is limited to a power of 2. To divide a range into three, it is split into four and one piece is left unused.
- In VLSM, larger pieces are placed first so that each sits on its boundary without leaving gaps. If the requirements are all the same size, changing the order makes no difference.
- The size to allocate is found by adding 2 to the required number of devices and rounding up to a power of 2. 100 devices become 102, rounded up to a piece of 128 addresses; 130 devices become 132, rounded up to a piece of 256 addresses.
- Once the size of a piece is fixed, the number of devices it can hold is two less than its number of addresses. The network address and the broadcast address are subtracted.
09Cloud Reserved AddressesHow They Work
When a subnet is created in a virtual network, the number of usable hosts can be lower than the usual calculation gives. This is because the platform sets aside some addresses for its own functions. The number deducted and the smallest size that can be created are linked.
When a subnet is created in a virtual network, the number of usable hosts can be lower than the usual calculation gives. This is because the platform sets aside some addresses for its own functions. The number deducted and the smallest size that can be created are linked.
On a physical network, two addresses are deducted: the network address and the broadcast address. In a virtual network, addresses used by the platform are reserved in addition.
The reserved addresses are, in most cases, a few consecutive addresses at the start of the subnet and the last one. The ones at the start hold the addresses of functions the platform provides, such as the subnet's default gateway and the address that receives name resolution queries. Some are kept free for features added in the future. The last one is reserved because it sits where the broadcast address would be. Whether broadcasts are actually delivered inside the virtual network is a separate question; the address is excluded from allocation either way.
Because the number of reserved addresses is fixed, subnet size has a lower limit. For example, if five addresses are reserved, including the network address and the last one, a subnet of 16 addresses keeps 11, but a subnet of 8 addresses keeps only 3. The smaller the subnet, the larger the share taken by the reservation. The platform sets the minimum size that can be created just before the remaining count would become too small for practical use.
An upper limit is also set. Unlike the lower limit, the upper limit is set independently of the number of reserved addresses.
The number of reserved addresses, the minimum size and the maximum size differ from platform to platform.
Key points
- Even when the same number is deducted, the smaller the subnet, the greater the impact. With five addresses deducted, a 256-address subnet loses just under 2 percent, while a 16-address subnet loses more than 30 percent.
- The reserved addresses are concentrated at the start and the end. Addresses in the middle of the subnet are not normally taken.
- The minimum size that can be created is not necessarily derived mechanically from the reserved count. It is sometimes set at a point that leaves a margin in the number of remaining addresses.
- The address space seen from outside the virtual network does not change, whether or not addresses are reserved. They are removed from what can be allocated, not from the range itself.
10How IPv6 WorksThe Subtraction Disappears
IPv6 is not simply an extension that makes addresses 128 bits long. The broadcast mechanism itself is gone, and so is the subtraction used to find the number of usable hosts. The way addresses are counted and written has also changed to fit numbers of this magnitude.
IPv6 is not simply an extension that makes addresses 128 bits long. The broadcast mechanism itself is gone, and so is the subtraction used to find the number of usable hosts. The way addresses are counted and written has also changed to fit numbers of this magnitude.
An IPv6 address is 128 bits long and is written as eight 16-bit groups of four hexadecimal digits separated by colons. Leading zeros in each group can be omitted, and a run of all-zero groups can be collapsed with a double colon. However, a double colon can be used in only one place. If it appeared in two places, there would be no way to work out how many groups each one stands for.
IPv6 has no broadcast address. To reach every node, the multicast address for that purpose is used as the destination. With multicast, only the nodes that have chosen to receive an address process it, so delivery can be narrowed down by purpose. With this change, there is no longer any reason to reserve the last address of a subnet.
Nor does the pattern corresponding to the network address need to be set aside for broadcast. The “minus 2” that was taken for granted in IPv4 is not applied in IPv6. However, the address whose interface ID is all zeros is reserved by RFC 4291 (February 2006) to designate the routers on that subnet.
The magnitude of address counts changes too. A single /64 subnet contains 18,446,744,073,709,551,616 addresses. Compared with roughly 4.3 billion for the whole of IPv4, the difference in scale is clear. This value is one more than the largest number an unsigned 64-bit integer can hold, so a representation that does not overflow has to be chosen when handling it.
Ranges are also defined for particular uses. fe80::/10 is link-local, valid only within the same link; fc00::/7 is for use within organizations; and 2001:db8::/32 is reserved for examples in documentation. What is actually allocated for use within organizations is the fd00::/8 half of fc00::/7.
Key points
- A double colon can be used in only one place. With two, the number of omitted groups cannot be recovered, and the address cannot be told apart from others.
- IPv6 does not subtract for broadcast. However, the address whose interface ID is all zeros is reserved to designate the routers on the subnet.
- A /64 contains 18,446,744,073,709,551,616 addresses. Because this is one more than the largest value an unsigned 64-bit integer can hold, a representation that does not overflow is needed.
- In place of broadcast, there is a multicast address for all nodes. The purpose carries over; only the mechanism has changed.
The app has all 11 topics, free and readable offline, including one on how individual cloud platforms reserve addresses. Examples in each topic open straight in the calculator. See SubnetDeck
Playbooks
IP addressing playbooks.
69 playbooks in 9 categories, each showing how to allocate addresses for a common situation. The 13 free ones are here in full.
Choosing between 10/8, 172.16/12 and 192.168/16, and where to carve from
What to base the top-level split of 10/8 on
10.0.0.0/8Free
Scenario
You are defining the corporate address space from scratch. There are 150 sites and 16 plants, and the cloud virtual networks go in the same space. Business units are reorganized every few years, and the regions that sites belong to change too. You are at the stage of deciding, first of all, what goes where in 10/8.
Assumptions
You can carve up 10/8 freely within your own company. For now, you do not need to consider that a future integration might mix this space with another company's. More kinds of purpose can be added later. You can count the filter lines that reference the boundaries.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Data center servers | 3,000 | |
| Enterprise-wide management and monitoring | 1,000 | |
| Remote access pool | 1,000 | |
| Boundary and handoff | 500 | |
| Enterprise-wide spare | 250 |
Reasoning
The first thing to decide in 10/8 is what the second octet means. There are three candidates: split by purpose, by organization, or by geography.
In short, split by purpose. Organizations and geography change, but purposes do not. Business units are reorganized every few years, and regional responsibilities get reshuffled. By contrast, a plant never turns into an office site, and a test environment never becomes production.
If you split by organization, every reorganization forces a choice: move the boundaries, or leave names that no longer match reality. The latter is almost always chosen, and a few years later a different department is sitting in the sales block. At that point, the divisions in the design document and what is actually on the devices no longer agree.
The top-level boundaries cannot be moved, because filters are written on the assumption that 10.16.0.0/12 is the plants. If a boundary moves, every line that references it has to be reviewed. With 150 sites, 16 plants, and the cloud, that means hundreds of lines, and unless they are all switched at once, there will be a window in which traffic passes in only one direction.
So keep what you decide up front to a minimum. Splitting 10/8 on /12 gives 16 blocks to hand out to purposes. Start with four purposes, and add one block when you run out. Blocks are only ever added, so existing boundaries never move. Using only 4 of 16 blocks looks wasteful, but not having to move anything is worth more.
Room to grow
There are 16 /12 blocks. The four purposes (enterprise-wide shared, sites, plants, and cloud) use four blocks, leaving twelve free. When adding a purpose, hand it a free block such as 10.64.0.0/12 and leave existing boundaries alone. Purposes that appear later, such as testing or IoT, also take a new block rather than splitting an existing one. Which block to hand out next is decided when it is needed.
Pitfalls
- Splitting the second octet by organization. Organizations are reorganized every few years but boundaries cannot move, so names drift away from reality and stay that way. Split by purpose instead.
- Defining many fine-grained purposes from the start. Not only do unused blocks pile up, but every new request needs a decision about which purpose it belongs to. Start with about four and add more when needed.
- Borrowing part of a neighboring block for a purpose that has run out. A boundary appears in the middle of the block, and from then on that block alone mixes two purposes. If a purpose runs out, hand it a whole block.
- Recording only the result of the split, not the reasons. The next person can read which block is for what, but not why the split is by purpose, so proposals to re-split by organization keep coming up.
- Taking the enterprise-wide shared range last. The convenient blocks get handed out first, and enterprise-wide shared ends up scattered across distant blocks. Give enterprise-wide shared the first block.
192.168/16 is not yours alone
192.168.0.0/16Free
Scenario
A company of about 100 people keeps its field equipment and test devices in the 192.168 range. Whenever a site-to-site connection with a business partner or contractor comes up, the addresses conflict with the other party's premises and have to be sorted out. Remote-work connections sometimes conflict with employees' own wireless routers as well.
Assumptions
The addresses used on the other party's premises cannot always be learned in advance. Devices that are routed to the outside can be separated from those that are not. Changing a device's address later requires an on-site visit and reconfiguration. 10/8 is also available for use.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Field equipment (not routed outside) | 200 | |
| Devices under test and before deployment | 200 | |
| Individual test benches | 100 | |
| Spare (inside the half in use) | 250 |
Reasoning
192.168.0.0/16 is not yours alone. Home devices, employees' own wireless routers, and the premises of partners and contractors all use the same space. It is well known that defaults cluster on 192.168.0 and 192.168.1, but the problem does not stop there. Small devices also default to 192.168.10, 192.168.100, and others, and you usually cannot find out in advance what the other party uses.
If you work around each block that conflicts, the record of avoided blocks keeps growing. After ten years of operation it runs to dozens of blocks, and every new partner has to be checked against the list. People do the checking, so things get missed.
So turn it around. Fix the range you use by its high-order bit, and claim only the half where the third octet is 128 or above. You give up half the space, but the decision is made once. A company of about 100 people needs fewer than 10 blocks, so 128 is more than enough.
Also limit what goes there. The only things allowed in this space are those that are not routed to other companies or other sites. If you know that conflicts in this space cannot be avoided, put only things there that do not suffer when a conflict happens. Anything visible from the far end of a site-to-site connection, or exposed to an interconnection, takes addresses from 10.0.0.0/8.
Room to grow
The company uses only the half where the third octet is 128 or above, and uses 4 of those 128 blocks. The other half, 192.168.0.0/17, stays empty, and no block-by-block checking is done even as partners increase. The decision is a single check: is the third octet 128 or above? When something needs to be routed to the outside, it does not go in this space; it takes addresses from 10.0.0.0/8. Even as devices increase, the half in use is enough.
Pitfalls
- Carving on the assumption that all of 192.168 belongs to you. Every interconnection brings a conflict, each one is handled by avoiding a block, and the records of avoided blocks end up scattered. Fix the range you use by its high-order bit.
- Keeping a list of conflicting blocks to avoid. Every new partner requires a check against it, and because people do the checking, things get missed. Make the decision a single check of the high-order bit.
- Putting devices that are visible from outside in this space. When they conflict with the other party's premises, only your side can move, so you end up changing the devices' addresses. Take addresses for anything exposed to the outside from 10.0.0.0/8.
- Starting to use the unused half because leaving it empty feels wasteful. Blocks you start using cannot be taken back; you gain nothing and lose the simplicity of the decision. For about 100 people, 128 blocks are more than enough.
Addressing for one site, from SOHO to large offices
A single-site office of about 100 people
10.20.0.0/22Free
Scenario
A head office or branch office with around 100 employees on one or two floors. It uses both wired and wireless, and keeps a file server and a NAS on premises. This is the most typical setup.
Assumptions
At least one Layer 3 switch or VLAN-capable router is in place. DHCP can run either on a network device or on a server. Headcount may grow to 1.5 times its current size within three years.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Clients (wired) | 150 | |
| Servers | 20 | |
| Network device management | 30 | |
| Printers and multifunction printers | 15 | |
| Wireless clients | 200 | |
| Phase 2 (reserved for future growth) | 200 |
Reasoning
At around 100 people, the first question is whether a single /24 is enough. The answer: for wired alone it is, but the site must not be cut as a single /24 block. Wired clients alone fit in a /24 block. Once company smartphones and the wireless connections of laptops are counted, however, each person actually has two or three devices, and the 254 addresses of a /24 fill up quickly.
So reserve a /22 and cut it internally into /24 and /26 blocks. Wired clients and wireless each get their own /24 so that exhaustion of one DHCP pool does not spill over into the other. Servers and management stay at /26 because at this scale they rarely exceed 60 devices, and allocating more would cost the readability of the third octet.
Giving the third octet a meaning is also deliberate. With 0 = wired, 1 = static-IP devices, 2 = wireless and 3 = phase 2, a glance at a packet capture or a log tells you which segment an address belongs to. This readability translates directly into faster troubleshooting.
Room to grow
Because 10.20.3.0/24 is left entirely free, even if headcount grows 1.5 times you can either widen wireless to a /23 or add one departmental segment. If the servers' /26 gets tight, move the printers in 10.20.1.128/27 over to 10.20.1.192/27, then move device management into the freed 10.20.1.128/26; the servers can then double to 10.20.1.0/25. To add another site, continue with 10.21.0.0/22, 10.22.0.0/22 and so on, and aggregate them as 10.20.0.0/14.
Pitfalls
- Using 192.168.1.0/24 or 192.168.0.0/24 on the corporate network. These conflict with the defaults of home routers, so routing breaks when people connect over VPN from home. Carve from 10/8 instead.
- Putting wireless and wired clients in the same segment. When you later want to add a guest SSID, the addressing plan has to be redone. Separating them from the start costs almost nothing.
- Mixing the management addresses of network devices into a client segment. ACLs can no longer restrict management access on its own, and audits will always flag it.
- Using the spare /24 for an immediate need “because it is free.” A spare is valuable precisely because it stays unused. Name it “phase 2” rather than “spare”; it is then more likely to be respected.
A hot-desking site where attendance is unpredictable
10.16.8.0/21Free
Scenario
A site of about 100 seats with no assigned desks. Against a headcount of 120, office attendance swings between 40% and 80% from day to day. Everyone carries a laptop, and wired ports remain only in meeting rooms and at a few fixed desks. About 10 short-term staff, such as agency workers and on-site contractors, are present at any time.
Assumptions
Wireless covers the whole site, and employees can do all their work on their devices over wireless alone. The DHCP lease time can be set per segment. Actual daily attendance can be retrieved afterwards, for example from entry and exit records. No desk booking system is in place.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Wireless pool for employee devices | 300 | |
| Reserved for merging into the pool (joins the wireless pool on expansion) | 400 | |
| Wired (meeting rooms, fixed desks) | 50 | |
| Short-term staff and guest devices | 40 | |
| Servers and shared devices | 20 | |
| Printers and multifunction printers | 12 | |
| Network device management | 12 | |
| Reserved for adding a second floor | 200 |
Reasoning
When sizing the pool, the first numbers that come up are the 100 seats and the headcount of 120. Drop the seat count first. Next comes the number of devices at peak attendance: at 80% attendance that is 96 people, and since each carries a laptop and a company smartphone, 192 devices. Up to this point, the 254 addresses of a /24 are enough.
This is where the estimate goes wrong. With hot desking, nobody knows who will come in today. With a 24-hour lease time, the addresses of devices belonging to people who came yesterday but not today are still alive. Attendance swinging between 40% and 80% means there are days when few of the same people come in two days in a row. If a 40% day (48 people) is followed by an 80% day (96 people) with almost no one in common, the number of people who came over the two days approaches the headcount of 120, and live leases reach up to 240 devices. That is 94% of the 254 addresses in a /24, leaving only 14. Exhaustion does not come on the most crowded day; it comes on the day the people change. What must be counted is not peak attendance but the number of people who could come within one lease time, in other words a number close to the headcount.
Could the lease simply be shortened? There is a lower limit. Laptops closed over lunch and afternoon meetings go silent for three to four hours, so with a 2-hour lease some devices pick up a different address when they come back. The pool size sets the upper limit on the lease time, and the way people work sets the lower limit. The only way to satisfy both is a /23 for the pool. With 510 addresses, 53% remain free even at 240 devices.
Taking a /23 breaks the match between the third octet and the segment, but at this site avoiding exhaustion takes priority over readability. Devices that communicate while constantly on the move need a separate decision if they are to share the same pool.
Room to grow
The adjacent 10.16.10.0/23 is kept free not for some future need but so that the pool can grow as a single subnet. A pool cannot be extended by adding separate pieces, so turning the /23 into a /22 requires the entire adjacent /23 to be free. The trigger is set at a headcount of 210 because if almost everyone comes in over two days, that means 420 devices, 82% of the 510 addresses in the current /23 block. At that point, merge the adjacent block to form 10.16.8.0/22 and leave the lease time as it is. This constraint is why wired and servers have been pushed out to 10.16.12.0/24. Unless the conditions for releasing the free space are decided in advance, it will always be taken for some other use.
Pitfalls
- Sizing the pool by seat count. If a /25 is cut because there are 100 seats, it falls short as soon as two devices per person and the short-term staff are counted, and the pool runs out in the first week of operation. Count devices, not seats.
- Shortening the lease time to speed up turnover and avoid exhaustion. Devices coming back after lunch or a meeting pick up a different address and lose their connections, but since the drop happens only at the moment they come back, it cannot be reproduced and never gets reported.
- Putting short-term staff devices in the same pool as employees. The device count estimated from headcount keeps drifting from reality, and with each increase in staff nobody can explain how many addresses were short. Keep what can be predicted apart from what cannot.
- Keeping the practice of assigning static IPs to wired ports. With hot desking, a different person sits at the same port every day, so the mapping between addresses and users soon breaks down and only the address register remains. Serve wired ports by DHCP as well.
Mapping site numbers to addresses, allocated for route aggregation
Numbering 150 sites so that route aggregation works
10.0.0.0/8Free
Scenario
150 sites in total: 1 head office, 8 regional hubs, and 141 sales offices and warehouses. Each site connects to the head office through a regional hub, and routes are aggregated at the regional hubs and passed upstream. Site numbers are already used in asset management and in forms and reports, and were assigned in order of opening. A few sites open and a few close every year.
Assumptions
Each regional hub can advertise the sites under it as a single route. A site numbering scheme already exists, and sites cannot be renumbered for the sake of the addressing plan. No site has more than 1,000 devices. Which region each site belongs to stays the same for years at a time.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Representative site (region 3, site 12): wired clients | 200 | |
| Representative site: wireless clients | 250 | |
| Representative site: servers and multifunction printers | 50 | |
| Representative site: network device management | 60 | |
| Representative site: spare within the site | 250 | |
| Inter-site links and loopbacks (block shared by all sites) | 250 |
Reasoning
Aggregation is what keeps 150 sites from going upstream as 150 routes. But what aggregation needs is contiguous address blocks, not contiguous site numbers. Get this wrong and the whole design is wasted.
The site numbers already exist. They are used in asset management and in forms and reports, were assigned in order of opening, and have no relation to regions. Map them straight onto the second octet and the hub for region 3 ends up holding a scattered set such as sites 3, 17, 42 and 88. Scattered blocks do not combine into one route, so 150 routes still go upstream. Renumbering for aggregation is not an option: the numbers are embedded in forms, reports and the names people use.
So reverse the order. Assign blocks first to the unit of aggregation, the regional hub, and hand out site numbers as identifiers inside that block. Each of the 8 regions gets one second octet, and each site gets one /22 block. A region holds up to 64 sites. With 150 sites even the largest region has only 24, so everything fits, and 8 routes go upstream. Even if the sites double to 300, it stays at 8.
The cost is that the site number can no longer be read from the address. Making it readable means giving up contiguity within regions. What incident response needs is not a numbering rule but one table that maps site numbers to blocks.
Room to grow
Regional blocks use second octets 1 to 8, and 0 is used for enterprise-wide shared purposes. The seven blocks 9 to 15 are kept free, for adding regions and for a second regional block given to any region that exceeds 64 sites. Those numbers are not contiguous, so look them up in the mapping table. Everything from 10.16.0.0/12 upward is left untouched and kept for acquisitions and for taking in other businesses.
Pitfalls
- Mapping site numbers directly to addresses. The numbers follow the order of opening and have nothing to do with regions, so the sites under one hub end up scattered and as many routes as there are sites still go upstream. Hand out numbers inside the regional block.
- Taking inter-site link addresses from the site's own block. When the other end is a site in another region, addresses from this region's block end up in that region, and more specific routes for them go upstream. Take links from a shared block outside the site blocks.
- Adding segments inside a site across the boundary of the site block. The part that spills over is not covered by the aggregate, and a more specific route for that one site goes upstream. Add only inside the block, and give a second block once it is exceeded.
- Requiring that the site number can be read from the address. Making it readable means giving up contiguity within regions, and aggregation stops working. Keep a mapping table instead of a numbering rule.
- Homing a single site on a different regional hub for geographic convenience. Its addresses stay in the original regional block, so upstream sees the regional block alongside a separate route for that one site. If a site's hub changes, move its addresses with it.
Pools for /30, /31 links and /32 loopbacks
Choosing /30 or /31 for point-to-point links
10.161.0.0/16Free
Scenario
In a network with 300 or more point-to-point links, you need to settle the prefix length for links. The devices span several generations: older equipment, special-purpose appliances, and virtual devices sit side by side. Standardizing on /31 has been proposed as a way to save addresses.
Assumptions
The model and generation of the devices at both ends of each link can be listed. Whether a device handles /31 can be checked in advance. Allocation is done in one place. Changing a link's addresses later requires rewriting device configurations and monitoring.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Link range cut as /30 (default) | 2,000 | |
| Link range cut as /31 (sections with confirmed support) | 250 | |
| Loopbacks | 250 | |
| Spare for links | 2,000 |
Reasoning
A /30 has four addresses, only two of them usable; a /31 uses both of its two. The number of addresses needed is halved.
As a saving, though, this means nothing. With 352 links, /30 takes 1,408 addresses and /31 takes 704. The difference of 704 is only about 1 percent of the /16 block set aside for links. A difference that small is no reason to change the decision.
The deciding factor is whether every device can handle it. Not every device supports /31 links. Older equipment, special-purpose appliances, or virtual devices may lack support. A link has one device at each end, so if even one of them lacks support, that link has to be a /30 link anyway.
Mixing the two changes the allocation procedure. The pool then holds two sizes, and every allocation requires checking support on the devices at both ends. At 10 links a month, that is 120 checks a year. Saving 704 addresses is not worth 120 checks a year.
So standardize. If every device supports it, use /31; if even one device without support remains, use /30 for every link. If mixing is unavoidable, split the sizes into separate ranges so that no check is needed at each allocation.
One more point. A link once cut as a /30 does not move to /31 even when its devices are replaced. Moving it means changing its addresses, which rewrites configurations and monitoring names. Do not plan on a later migration.
Room to grow
The default is /30, and only sections with confirmed support are cut from the /31 range. The ranges are split so that allocation never requires checking device support. A section is added to the /31 range only when the devices at both ends have been replaced and their support confirmed. Growth comes from 10.161.16.0/21. Even after every device has been replaced, existing /30 links are not converted; only newly created links are cut as /31 links.
Pitfalls
- Choosing /31 to save addresses. The saving is about 1 percent of the link block and no reason to change the decision. Base the decision on whether every device supports it.
- Mixing both sizes in the same range. Every allocation then needs a support check on the devices at both ends, adding 120 checks a year at 10 links a month. If you must mix, use separate ranges.
- Making /31 the default while one device still lacks support, with only that section kept as a /30 exception. Every device replacement then needs a support check, and missing it even once leaves that link unusable. Make /30 the default, and cut /31 links only from the range for sections with confirmed support.
- Choosing /30 on the assumption of moving to /31 later. Moving means changing addresses, which rewrites configurations and monitoring names. Decide on the assumption that links will never move.
DMZ, servers, clients, management, voice and guest Wi-Fi
Share nothing between guest wireless and the corporate network
172.30.0.0/16Free
Scenario
A company of about 100 people is setting up guest wireless. On normal days there are about 20 guest devices, but on days with information sessions or exhibitions, 400 arrive at once. Traffic to the corporate network is blocked by filters, but name resolution and address assignment run on the same equipment as the corporate network.
Assumptions
Guest wireless can be offered as a range separate from corporate wireless. A single outbound exit can be provided for guests. Separate name resolution and address assignment equipment can be set up for guests. There is a usable position within 172.16/12.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Guest devices | 400 | |
| Guest exit and address assignment equipment | 10 | |
| Guest name resolution (external lookups only) | 5 | |
| Expansion block for events | 800 |
Reasoning
The usual assumption is that guest wireless only needs to be cut off from the corporate network: block traffic to the corporate network with filters and the job is done. That is not enough.
The guest range also shares things with the corporate network outside the filters. If guests resolve names through corporate equipment, guest devices can query the names of corporate servers. Even when no answer comes back, the response to a query shows which names exist. If addresses are assigned by the same equipment as the corporate network, then on an event day when 400 devices come to a 100-person company, corporate address assignment chokes as well. If guests are made to sync their clocks to the corporate network, a route to the corporate time server has to be opened.
So the guest range shares nothing with the corporate network. It has no route to any corporate segment, and its only exit is a single outbound one. Name resolution and address assignment are kept separately, for guests alone. Instead of blocking with filters, the routes that would need blocking are made not to exist at all. A blocked route can be opened with one line; a route that does not exist cannot be opened.
The choice of addresses has a reason too. Most guest devices open connections back to their own company. If that company uses 10/8 internally and the guest range is also in 10/8, addresses collide on the other side and the guest cannot reach their own company. The range is taken from a little-used position within 172.16/12.
Room to grow
The guest range has no route anywhere in the corporate network, and its only exit is a single outbound one. Name resolution and address assignment are also kept separately for guests. When events bring more devices, 172.30.4.0/22 is added to take them, and the added range leaves through the same exit. No routes to the corporate network are added. The range stays within 172.16/12 and does not overlap 10/8, which guests' companies are likely to use.
Pitfalls
- Relying on filters to stop traffic to the corporate network. If name resolution or address assignment is shared with the corporate network, internal information leaks outside the filters and load carries over too. Share nothing.
- Letting guest devices use corporate name resolution. Even without answers, the responses to queries show which names exist. Keep separate name resolution for guests.
- Running guest address assignment on the same equipment as the corporate network. When guests surge on an event day, corporate address assignment chokes too. Separate address assignment for guests.
- Taking the guest range from 10/8. When guests connect back to their own company, addresses collide with that company's internal network and the connection fails. Take it from a little-used position within 172.16/12.
Decide what belongs in the DMZ and how to split it
10.170.0.0/16Free
Scenario
At a company of about 500 people, the equipment placed in the DMZ grows every year. A public-facing web server, a server for exchanging files with business partners, equipment that receives mail from outside, a server that only calls external services, and equipment that sends monitoring alerts out all share one range.
Assumptions
Equipment that receives connections initiated from outside can be told apart from equipment that only sends traffic out. The counterparts of each business partner connection can be identified. DMZ ranges can be provided separately per counterpart. Traffic between ranges can be stopped at the boundary.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Public-facing (anyone can connect) | 20 | |
| Partner-facing (known counterparts) | 20 | |
| Equipment receiving mail from outside (range split off from public-facing) | 10 | |
| DMZ spare | 100 |
Reasoning
There is one criterion for what goes in the DMZ: equipment that receives connections initiated from outside.
Without a criterion, everything that talks to the outside ends up there: equipment that only sends traffic out from inside, servers that only call external services, equipment that sends monitoring alerts out. None of these receive connections initiated from outside, so there is no reason to place them in the DMZ. Placing them there makes the DMZ grow, and when any one of them is compromised, everything next to it becomes reachable.
Once what goes in is decided, the next split is by who it receives from. Public-facing and partner-facing equipment do not share a range. Anyone can reach the public-facing side, so it is designed on the assumption that it will be compromised. The partner-facing side has known counterparts, so its permissions are far narrower. If the two share a range, a compromised public-facing server can reach the files exchanged with partners from right next door. Restricting the counterparts then means nothing.
Traffic between the separated ranges is not allowed. There is not a single business reason for the public-facing side to reach the partner-facing side.
When new equipment that receives from outside appears and it is unclear who it receives from, it goes into the public-facing range. Putting equipment whose counterparts cannot be restricted into the partner-facing range breaks the premise of that range.
Room to grow
The DMZ is split by who each range receives from, with public-facing and partner-facing equipment in separate ranges. Traffic between ranges is not allowed. When new equipment that receives from outside appears, its range is decided by who it receives from, and if that cannot be decided, it goes into the public-facing range. When ranges run short, they are cut from 10.170.1.0/24. Equipment that only sends traffic out stays out of the DMZ no matter how much of it there is.
Pitfalls
- Putting everything that talks to the outside into the DMZ. Once equipment that only sends traffic out goes in too, the DMZ grows, and one compromise reaches everything next to it. Place only equipment that receives connections initiated from outside.
- Putting public-facing and partner-facing equipment in the same range. When the public-facing side is compromised, the files exchanged with partners can be reached from next door. Split ranges by who they receive from.
- Allowing traffic between the separated ranges just in case. A permission with no business reason only becomes a path for an intruder. Allow nothing between ranges.
- Putting equipment with unclear counterparts in the partner-facing range. That range keeps its permissions narrow on the premise that its counterparts are known, and the premise breaks. When in doubt, use the public-facing range.
Sizing subnets around addresses the platform reserves
Count five fewer addresses in cloud subnets
10.216.0.0/16Free
Scenario
You are creating a small subnet for 10 devices in each failure zone of a cloud virtual network. Thinking as you would on the corporate network, you expect a /28 to hold 14 devices. An application subnet of about 200 hosts is also planned for the same virtual network.
Assumptions
You know that your provider takes some addresses inside each subnet in advance. You can check how many it takes and the smallest subnet size it allows. A subnet's size cannot be changed after it is created. The virtual network has free space.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Subnet for 10 devices (27 usable after reservations) | 10 | |
| Same purpose in another failure zone | 10 | |
| Application subnet (reservations are a small share) | 200 | |
| Spare subnets | 100 |
Reasoning
When you create a subnet in the cloud, the provider takes some of its addresses in advance. It varies by provider, but taking the first four and the last one, five in total, is common. On a corporate network only the first and last addresses are unusable, so carving subnets without knowing this difference leaves you short.
The difference hits small subnets hardest. In a /24 it is 5 of 256, under 2 percent. In a /26 it is 5 of 64, or 8 percent. In a /28, the smallest size you can create, 5 of 16 disappear, roughly 30 percent. Only 11 are usable.
Carve a /28 with corporate-network habits and you expect room for 14 hosts but can place only 11. With 10 devices, the margin is a single address, and the day you add two more, the subnet overflows. A subnet's size cannot be changed after creation, so an overflow means rebuilding it.
So when carving small subnets, compare the host count with the number left after reservations. For 10 hosts, take a /27 rather than a /28 subnet. A /27 leaves 27 usable after subtracting 5 from 32. The smaller the subnet, the larger the share lost, so as a rule small subnets are carved one size larger than on the corporate network.
The number of reserved addresses differs by provider, and so does the smallest size allowed. Choose a reservation profile in the Calculate tab and the usable count appears immediately. Check your estimates there.
Room to grow
For small subnets, subtract the 5 reserved addresses before comparing with the host count. For 10 hosts, take a /27 rather than a /28 subnet. Line them up at the same size, one per failure zone. When more subnets are needed, carve them from 10.216.2.0/24. If you are unsure about an estimate, choose the reservation profile in the Calculate tab and check the usable count.
Pitfalls
- Counting usable addresses with corporate-network habits. Subtracting only the first and last overlooks the other three the provider takes, and the planned number of hosts does not fit. Compare using the count after reservations.
- Making the smallest size, /28, the standard. Five of 16 disappear, leaving only 11 usable, and adding just a few hosts overflows it. For about 10 hosts, take a /27 subnet.
- Assuming a subnet can be enlarged later. Its size cannot change after creation, and an overflow means rebuilding it. Estimate with reservations included from the start.
- Assuming every provider reserves the same number. Providers differ both in how many addresses they take and in the smallest size allowed. Check with the profile for your provider.
Avoiding overlaps, VPN links and renumbering after a merger
When working around an overlap with translation, set the deadline at the same time
172.18.0.0/15Free
Scenario
You are connecting the network of a company you acquired to your own. Both use 10/8, and many ranges overlap. Business needs require the networks to be connected by next month, and there is no time to renumber either side. A proposal is on the table to connect them by translating addresses at the boundary.
Assumptions
One boundary that can translate addresses can be placed between the two companies' networks. Translated addresses can be taken from space outside both companies' address spaces. A deadline can be written into the translation rules. The side to renumber can be decided without waiting for a management decision.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Translated range for seeing the other company's network from yours | 3,000 | |
| Translated range for presenting your network to the other company | 800 | |
| Translation devices and management | 20 | |
| Translation spare (growth until the deadline) | 400 |
Reasoning
There are two ways to connect two overlapping networks: renumber one of them, or translate addresses at the boundary. Translation can be in place overnight; renumbering takes months. Choosing translation early in an integration is right.
The problem is that translation becomes permanent. Because traffic gets through with translation in place, the reason to renumber disappears. Three years later, translation rules have piled up and no one can explain them as a whole. At every incident, someone has to check whether an address in the logs is from before or after translation.
So on the day translation goes in, decide two things together: the deadline, and the side that will be renumbered. Set the deadline as a date and write it into the translation rules themselves. Decide the side to renumber that same day, and treat the translation period as preparation time for the renumbering. A translation with no decision on which side to renumber can only be extended when the deadline arrives.
Take the translated addresses from space that belongs to neither side. If both you and the other company use 10/8 and that is where the overlap is, take the translated addresses from 172.16/12. If you use free space in either side's 10/8, the next company you take in will overlap again.
Some translation can be permanent. When identical addresses repeating side by side is a premise of the design, as with production lines built from the same copied configuration, permanent translation is correct. An overlap in an integration is not a premise but an accident, and the remedy for an accident must not be made permanent.
Room to grow
Take the translated ranges within 172.16/12, and keep the range for seeing the other company's network separate from the range that presents your network to the other company. Write the deadline into the translation rules, and by the deadline renumber the side decided on the day translation went in. Carve any growth until the deadline from 172.18.24.0/22. Do not extend a translation past its deadline; if an extension is needed, start again from the decision on which side to renumber.
Pitfalls
- Not setting a deadline when translation goes in. Traffic gets through, so the reason to renumber disappears, and translation rules pile up until no one can explain them.
- Putting translation in without deciding which side to renumber. When the deadline comes, the discussion starts over from which side to move, so the only option is to extend. Decide on the same day as the translation.
- Taking translated addresses from free space in your own 10/8. The next time you take in another company, they will overlap again. Take them from space that belongs to neither side.
- Writing translation rules one host at a time. Deadlines then have to be managed one host at a time too, and no one knows which rules remain. Write them per range.
Static addressing on the control side, OT/IT separation and growth
A manufacturing cell design for replicating identical lines
172.20.0.0/16Free
Scenario
A plant has several production lines with the same equipment configuration and plans to add more. The controllers delivered by the equipment vendor have fixed IP addresses burned in, and you start from a state where the same addresses overlap between lines.
Assumptions
The controllers' addresses on each line cannot be changed, or changing them requires the equipment vendor to repeat acceptance testing. Lines do not need to talk to each other directly; they only need to talk to the upstream collection systems. A Layer 3 device or a device capable of NAT can be placed at each line boundary.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Line 1 (addresses seen from outside) | 200 | |
| Line 2 (addresses seen from outside) | 200 | |
| Line 3 (addresses seen from outside) | 200 | |
| Collection and monitoring servers | 30 | |
| Maintenance laptops (for PCs brought in) | 10 | |
| Reserved for line expansion (lines 4 to 7) | 1,000 |
Reasoning
What sets OT networks decisively apart from IT is that addresses cannot be chosen freely. Equipment vendors deliver the same configuration to many customers, so controller addresses are fixed at shipment, and the same 192.168.0.10 exists on line 2 and on line 3 alike. Apply the usual IT reflex, "it overlaps, so renumber it," and the discussion turns to equipment warranties and repeated acceptance testing while the floor stands still.
So do not renumber. Leave the addresses inside each line as the equipment vendor set them, apply 1:1 address translation on the device at the line boundary, and distinguish only the addresses seen from outside, by line number. A controller on line 1 appears from outside as 172.20.1.x, and the same device on line 2 as 172.20.2.x. With the rule that the third octet equals the line number, anyone reading the collection system's logs can tell the line at once without knowing device names.
The essence of this design is to separate the equipment vendor's constraints from IT manageability with a single layer: translation. Inside the line is the equipment vendor's world; from the boundary up is the IT department's world. The biggest advantage is that adding a line does not mean redoing the design: increment the number by one and copy the same configuration.
Room to grow
172.20.4.0/22 (lines 4 to 7) is reserved for the next expansions. Because the base block is a /16, the rule of using the third octet as the line number reaches line 255 (0 is not used as a line number and is set aside for shared collection and maintenance), and from line 8 on it continues naturally with 172.20.8.0/21 and 172.20.16.0/20. If more plants are added, the second octet becomes the plant number: 172.21.0.0/16 goes to the next plant, and both are aggregated as 172.20.0.0/15. A line outgrows its /24 only when it has more than 250 controllers, and at that scale the line is easier to operate if it is split logically.
Pitfalls
- Allowing traffic between lines "just in case." When one line is infected with malware, every line with the same configuration stops at once. Block traffic between lines by default and route the traffic that is needed through the collection systems.
- Providing no segment for maintenance laptops and plugging brought-in PCs straight into the control segment. This is the most common entry point for OT incidents, and it leaves no record. Create a dedicated segment and allow entry to the control side only from there.
- Keeping the address translation mapping table only in the device configuration. Once the person who set it up moves on, nobody can explain which outside address belongs to which piece of equipment. Keep the mapping table in the design documents as the primary record.
- Using the 192.168 range for plant addresses. It easily conflicts with the routers and mobile routers that maintenance vendors bring in, and the conflict only shows up on site. Carve plant addresses from 172.16/12 or 10/8 instead.
- Mapping line numbers to addresses by filling whatever number happens to be free at each expansion. When line 7 is removed and different equipment later takes its place, the numbers drift away from the physical lines and nobody trusts them. Never reuse a number.
A boundary zone that separates a plant's IT and control networks
10.60.0.0/20Free
Scenario
A plant of about 300 employees with an office building and a factory building on the same premises, run until now as a single network. Production management will still need to send instructions to the equipment and collect results from it, but office PCs must no longer be able to reach controllers directly. You are at the stage of redrawing only the boundaries above and below the lines first, without touching the design inside the lines.
Assumptions
At least one Layer 3 device can be placed between the office side and the plant side. Traffic crossing between the two sides can be listed, at least per handoff server, by peer and direction. Controller addresses are not changed this time, and the redesign inside the lines is done separately. The requirements include that production can continue while the boundary devices are down.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Office clients (wired and wireless) | 300 | |
| Production management and business servers | 40 | |
| Handoff servers (relays reached from both sides) | 12 | |
| Maintenance laptops on loan | 10 | |
| Management of boundary devices and monitoring | 6 | |
| Boundary phase 2 (external data links, remote maintenance relays) | 50 | |
| Control network shared services (time sync, name resolution, devices outside the lines) | 100 | |
| Control network wireless (material handling equipment, handheld terminals) | 200 | |
| Reserved for per-line zones (lines 1 to 4) | 1,000 |
Reasoning
Nobody objects to separation. What never gets decided is the size of the zone placed at the boundary.
Taking a /24 for the boundary always fails. At this scale, the only machines that truly need to talk to both sides are the handoff servers, a dozen or so. The remaining 240-plus addresses become empty lots, and empty lots always get filled. Six months later a business file server moves in; the following year, a jump server joined to the office authentication infrastructure. At that point the boundary is no longer a boundary, but nothing changes in the address table, so nobody notices.
That is why the handoff is held to a /28 and no larger. With only 14 addresses, whoever tries to place a fifteenth machine has to ask someone first. The aim is to make the size work as an operating rule. Room to grow is placed next door under a different name, for phase 2, and the handoff zone itself is never widened.
Splitting the /20 into three areas, 0 to 3 (IT), 4 to 7 (boundary), and 8 to 15 (control), is also deliberate. The boundary device's filters can be written in three lines, 10.60.0.0/22, 10.60.4.0/22, and 10.60.8.0/21, and those three lines stay the same as segments are added. With a design that touches the filters at every addition, someone will one day touch them wrongly and stop production.
The zone for the control network's shared services, a /25, sits on the control side for the sake of availability. Production continues while the boundary devices are down. If time synchronization and name resolution depend on the office side, a boundary outage becomes a control-side outage.
Room to grow
At the boundary, 10.60.4.64/26 is kept free for phase 2. It is not for widening the handoff zone but a place to add external data links and remote maintenance relays later. On the control side, 10.60.12.0/22 is kept free for per-line zones, and per-line designs go there. If the wireless outgrows its /24, add 10.60.10.0/23. If more plants are added, assign 10.60.16.0/20 to the next plant and aggregate them as 10.60.0.0/16. Because the edges of the three areas are aligned on /22 boundaries, the three filter lines take the same form at every plant.
Pitfalls
- Placing a jump server at the boundary and joining it to the office authentication infrastructure. This opens a path for credentials to flow in from the office side, and the boundary loses its meaning. If a jump server is placed there, keep its authentication closed inside the boundary.
- Leaving controllers pointed at an office-side server for time synchronization. The moment the boundary device is stopped, control-side clocks start to drift, and logs cannot be matched up when a failure is traced later. Put time synchronization on the control side.
- Defining the separation requirement only as "no entry from the office into the control network." Traffic from the control side to the office side goes unchecked, leaving a way out for a device slipped in among the equipment. Set rules for both directions.
- Having the handoff servers also do collection and file storage. The side that cannot be stopped keeps them from being updated, and within a few years nobody dares touch them. Split them by role and keep their count within the /28 limit.
Allocating /64s out of a /48, and growing as demand appears
Divide IPv6 by hex digits instead of conserving it
2001:db8:100::/48Free
Scenario
A company with 10 sites has received an IPv6 /48 from its ISP. With IPv4, it sized each subnet to its device count and paid close attention to where spare space went and to fragmentation. It is about to start allocating IPv6 with the same mindset.
Assumptions
A /48 has been received from the ISP. Devices in the company can use IPv6 automatic address configuration. The number of sites and the number of purposes are each expected to stay at 15 or fewer. Addresses are meant to be read by people, who take meaning from them.
Allocation
| Segment | Hosts | Block |
|---|---|---|
| Site 1 clients | 200 | |
| Site 1 servers | 50 | |
| Site 1 management | 30 | |
| Site 2 clients (other purposes follow the same pattern) | 200 |
Reasoning
A /48 contains 65,536 /64 subnets. Much of the thinking built up over years of IPv4 is reversed here.
In IPv4, subnet size was decided by device count: a /28 for 10 devices, a /24 for 200. IPv6 does not do that. Every subnet is a /64 subnet, regardless of device count. The mechanism by which devices choose their own addresses is built on the assumption of a /64 prefix. Cut smaller than a /64, and that mechanism stops working.
No conservation is needed either. Almost no organization will use up 65,536 /64 subnets. The problems that took so much effort in IPv4, such as where to put spare space and how to prevent fragmentation, all but disappear.
One decision remains: how to divide the 16 bits of the fourth 16-bit group. Here, 4 bits go to the site, 4 bits to the purpose, and 8 bits to a sequence number. When the boundaries between meanings fall on the boundaries between hex digits, an address can be read at a glance. 2001:db8:100:1200::/64, for example, is the first server subnet at site 1.
Align the divisions with hex digits. Divide in the middle of a hex digit, and every reading of an address means converting it to binary, which throws away the benefit of readability. If the number of sites may exceed 15, give the site 8 bits from the start and 4 bits each to the purpose and the sequence number.
Room to grow
The first hex digit of the fourth 16-bit group is the site, numbered from 1, with 0 kept for company-wide use. The second digit is the purpose and the last two are the sequence number. Subnets are always /64 subnets and do not grow when devices increase. The /64 subnets in the segment table look large for their device counts because the protocol requires a /64 prefix, not because extra room was taken. If sites exceed 15, keep the divisions as they are and obtain a second /48 prefix.
Pitfalls
- Sizing subnets by device count and cutting them smaller than a /64 subnet. The mechanism by which devices choose their own addresses assumes a /64 prefix and stops working. Always use /64 subnets.
- Packing subnets tightly out of concern for spare space and fragmentation, as in IPv4. Using up 65,536 /64 subnets is almost unheard of, and packing gains nothing. Put readability first.
- Dividing the fourth 16-bit group in the middle of a hex digit. Every reading of an address means converting it to binary, and meaning can no longer be read from the address. Divide on hex digit boundaries.
- Numbering the site digit from 0. There is no place left for company-wide use, and it has to be squeezed in later. Keep 0 for company-wide use.
The other 56 playbooks can be read in full in SubnetDeck with Premium.See SubnetDeck
SubnetDeck for iPhone and iPad
The calculator you trust, with a memory.
This page forgets everything when you close it. SubnetDeck keeps a design plan for every site, in folders by customer or project — and it never goes online.
- Folders per site, customer or project, searchable by address
- VLSM allocation from host counts, with overlap detection
- Equal split, route aggregation and overlap check as tools
- Export plans to .xlsx, CSV or Markdown
- 69 playbooks and 11 Learn topics, readable offline
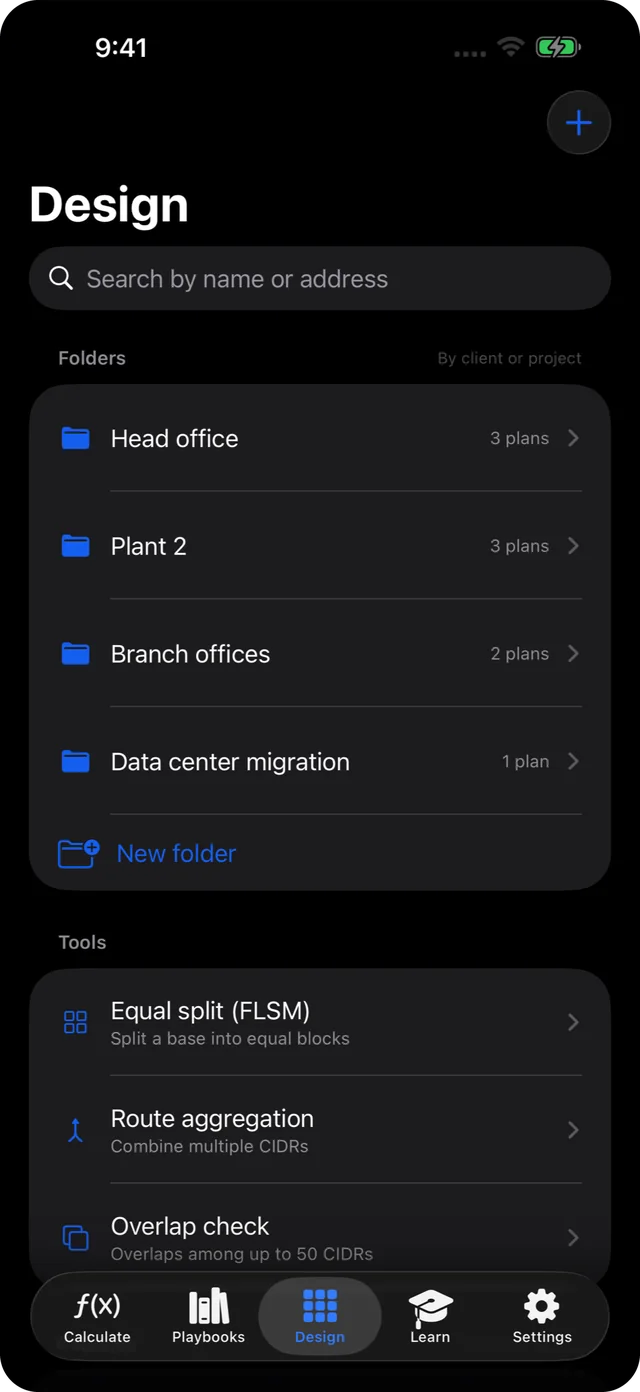
Scan with your iPhone to open the App Store.
Web and app, side by side
| This site | SubnetDeck app | |
|---|---|---|
| IPv4 / IPv6 subnet calculation | ✓ | ✓ (offline) |
| Special-purpose ranges (IANA) | ✓ | ✓ |
| Split a block | Try it, not saved | Equal split and VLSM, saved in plans (Premium) |
| Keep plans per site or customer | — | Premium |
| Export .xlsx / CSV / Markdown | — | Premium |
| Playbooks | 13 free | 13 free, 69 with Premium |
| Learn topics | 10 | 11 |
| Works with no connection | — | ✓ |
FAQ
Questions.
Is what I type sent anywhere?
No. All calculation runs in your browser with JavaScript. The page shows no ads and sets no cookies, and the address you enter only appears in this page's URL after the # sign, which browsers never send to the server.
Why does /31 have 2 usable hosts?
A /31 is used for point-to-point links, where no broadcast address is needed, so both addresses can be assigned (RFC 3021). A /32 is a single host. The Learn topic “/31 and /32” explains why the usual subtraction breaks down.
Can I enter a mask or a wildcard instead of a prefix?
Yes. “192.168.1.0 255.255.255.0”, “192.168.1.0 0.0.0.255” and “192.168.1.0/255.255.255.0” all work. A mask or wildcard on its own shows its prefix and host count. A range such as “10.0.0.5 - 10.0.0.90” becomes the exact list of CIDR blocks that covers it.
Why is there no broadcast address for IPv6?
IPv6 has no broadcast; multicast takes its place. Every address in an IPv6 block is counted as usable. The all-zero address is the subnet-router anycast address but is not deducted (RFC 4291).
How is the special-purpose type decided?
From the IANA IPv4 and IPv6 Special-Purpose Address Registries, using the longest match. The table was last checked against the registries on 2026-09-23.